Category: Uncategorized

  • Apple starts checking your age before you download these apps

    Apple starts checking your age before you download these apps

    Apple just started blocking certain app downloads in three countries. Users in Brazil, Australia, and Singapore now face automatic age checks when trying to download apps rated 18+ from the App Store.

    The move is part of a broader effort to comply with child safety laws worldwide. Apple told developers about the changes Tuesday, expanding its age assurance tools to meet new rules in the US and abroad.

    For affected users, the process is automatic. The App Store checks your age in the background before letting you download mature content. Developers still have their own compliance duties to handle.

    How the new blocks actually work

    The block happens instantly when you try to download an 18+ app. You don’t need to upload an ID or prove anything manually. Apple just confirms your age using your account details.

    But developers aren’t off the hook. They still need to meet any age verification requirements their local laws demand.

    For gamers in Brazil, the rules are stricter. Apps with loot boxes now carry an automatic 18+ rating, keeping kids away from gambling-like mechanics.

    The bigger shift happening behind the scenes

    These three countries aren’t the only ones. Apple is also expanding tools in the US, with new users in Utah and Louisiana soon having their age range shared with developers.

    The company is beta testing an updated Declared Age Range API. It gives developers a user’s age bracket without revealing their exact birth date. It’s a privacy-focused fix for a growing problem, as more governments pass laws restricting kids from certain apps.

    What comes next for Apple’s age checks

    This won’t be the last expansion. Apple moves quickly when new laws take effect. The company worked on similar requirements in Texas last year but paused in December while that law faces a court challenge.

    Apple isn’t alone in racing to build these tools. ChatGPT started rolling out age prediction in January, analyzing account behavior to estimate whether someone’s under 18 and automatically applying content filters. Users flagged incorrectly can verify their age through Persona, an identity service that uses live selfies and government IDs.

    Discord took a different path. The platform announced global age verification in February but quickly delayed it to late 2026 after users pushed back over privacy concerns.

    For now, the strictest rules apply in Brazil, Australia, and Singapore. But the pattern is clear. More places are demanding age checks, and platforms are scrambling to catch up. If you live elsewhere, expect changes when your local laws arrive.
  • Google Introduces New AI Marketing Tool for Small Businesses

    Google Introduces New AI Marketing Tool for Small Businesses

    Add Techlomedia as a preferred source on Google. Preferred Source

    Google has launched a new experimental AI tool called Pomelli. The tool is available through Google Labs and is built in partnership with Google DeepMind. It is designed to help small and medium businesses create professional marketing content using artificial intelligence.

    Pomelli focuses on making marketing easier for businesses that do not have large teams or big budgets.

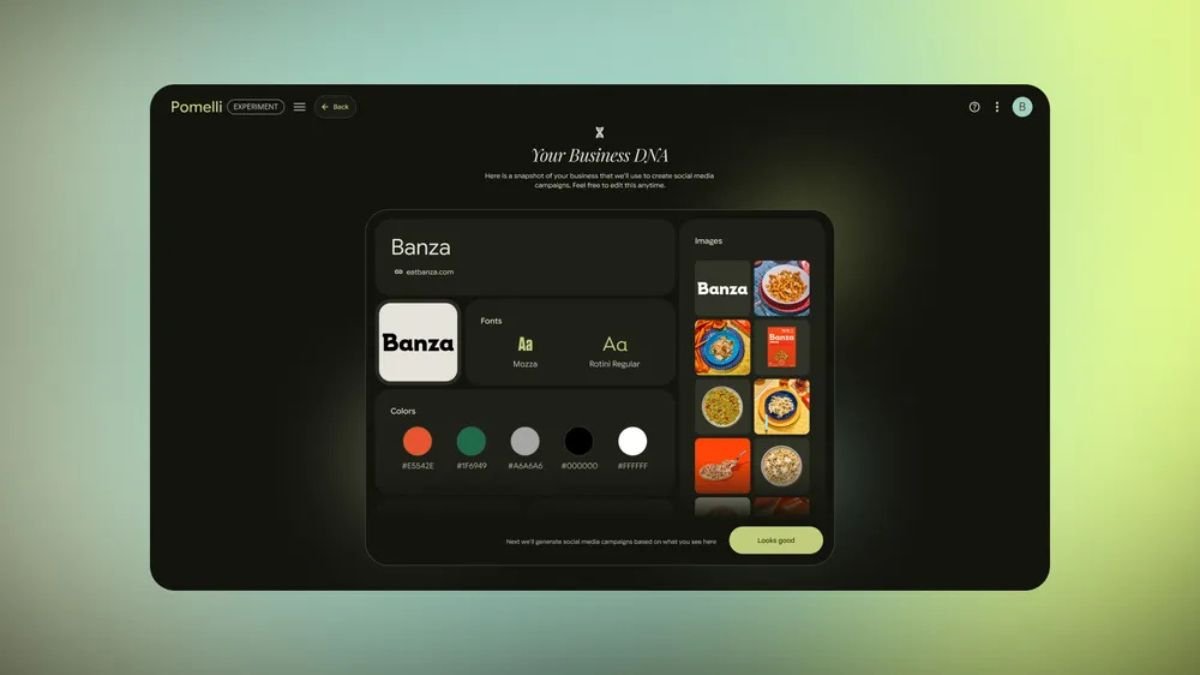
    Pomelli starts by understanding what Google calls your business DNA. Users need to enter their website URL. The tool then scans the site and studies elements such as tone of voice, fonts, images, and color palette. Based on this analysis, Pomelli generates marketing assets that match the brand’s identity. This can include campaign ideas, social media creatives, ad visuals, and even product photos.

    The goal is to make the content look consistent and professional without requiring advanced design skills.

    One of the most interesting features is the Photoshoot capability. With this feature, users can upload a simple product photo. Pomelli then enhances it into a more polished and studio-style image. This can help small businesses create high-quality visuals without hiring photographers or booking expensive studio sessions. The generated assets can be downloaded and used on social media, websites, and advertising campaigns.

    Users can also edit and refine the results to better match their preferences.

    Marketing is often expensive and time-consuming. Many small businesses struggle with content creation. Pomelli aims to reduce that gap by offering AI-driven support. Instead of designing everything from scratch, business owners can quickly generate on-brand content. This saves time and lowers cost.

    Early reactions on social media suggest that many users find the tool useful and creative. Some have shared examples of AI-generated product shots that look professional.

    At the moment, Pomelli is available as a public beta through Google Labs. It is currently limited to users in the United States, Canada, Australia, and New Zealand. The tool is available in English.

    There is no official word yet on when it will expand to other regions.

    Follow Techlomedia on Google News to stay updated. Follow on Google NewsFollow on Google News

    Affiliate Disclosure:

    This article may contain affiliate links. We may earn a commission on purchases made through these links at no extra cost to you.

  • PayPal Discloses Data Breach Linked to Internal Coding Error

    PayPal Discloses Data Breach Linked to Internal Coding Error

    Add Techlomedia as a preferred source on Google. Preferred Source

    PayPal has revealed a data breach that exposed sensitive customer information for more than six months. The company published a detailed disclosure report on its official website. It confirmed that a coding error in its PayPal Working Capital loan application led to the exposure. The issue lasted from July 1, 2025, to December 13, 2025.

    The company detected the problem on December 12, 2025. A formal written notification was sent to affected users on February 10, 2026, from its headquarters in San Jose, California.

    PayPal clarified that this was not the result of an external hacking attack. Instead, the exposure was caused by an internal software defect. A code change inside the PayPal Working Capital loan application interface unintentionally allowed unauthorized third parties to access customer data.

    Once discovered, the company rolled back the code change and ended the unauthorized access. PayPal also stated that no law enforcement investigation delayed the customer notification.

    The exposed data includes highly sensitive personal and business information. This may include full name, email address, phone number, business address, Social Security number, and date of birth. The combination of Social Security numbers and date of birth increases the risk of identity theft and financial fraud. It can also make affected users more vulnerable to social engineering scams.

    PayPal said that a small number of customers experienced unauthorized transactions. The company has refunded those users. A spokesperson stated that around 100 customers were potentially impacted.

    When there is a potential exposure of customer information, PayPal is required to notify affected customers. In this case, PayPal’s systems were not compromised. As such, we contacted the approximately 100 customers who were potentially impacted to provide awareness on this matter.

    After discovering the issue, PayPal launched a full investigation. The company terminated unauthorized system access and enforced mandatory password resets for affected accounts. Users were required to set new credentials during their next login.

    As part of remediation, PayPal is offering two years of free credit monitoring and identity restoration services through Equifax Complete Premier. The package includes up to one million dollars in identity theft insurance coverage.

    Affected customers must enroll using their activation code before July 31, 2026.

    PayPal is advising affected customers to review their transaction history and monitor their credit reports through annualcreditreport.com.

    Users can also place a fraud alert or credit freeze with the three major credit bureaus, including Equifax, Experian, and TransUnion. These services are available at no cost. The company also reminded users that it will never ask for account passwords, credentials, or one-time authentication codes through phone calls, texts, or emails.

    Follow Techlomedia on Google News to stay updated. Follow on Google NewsFollow on Google News

    Affiliate Disclosure:

    This article may contain affiliate links. We may earn a commission on purchases made through these links at no extra cost to you.

  • Xiaomi Tag Teased Ahead of Barcelona Debut

    Xiaomi Tag Teased Ahead of Barcelona Debut

    Add Techlomedia as a preferred source on Google. Preferred Source

    Xiaomi has officially confirmed its entry into the Bluetooth tracker market. The company has announced the Xiaomi Tag, which will compete with the Apple AirTag. The new tracker will make its global debut alongside the Xiaomi 17 series later this week.

    The launch event is scheduled for February 28, 2026, at 2:00 PM GMT in Barcelona. For Indian viewers, the event will begin at 7:30 PM IST.

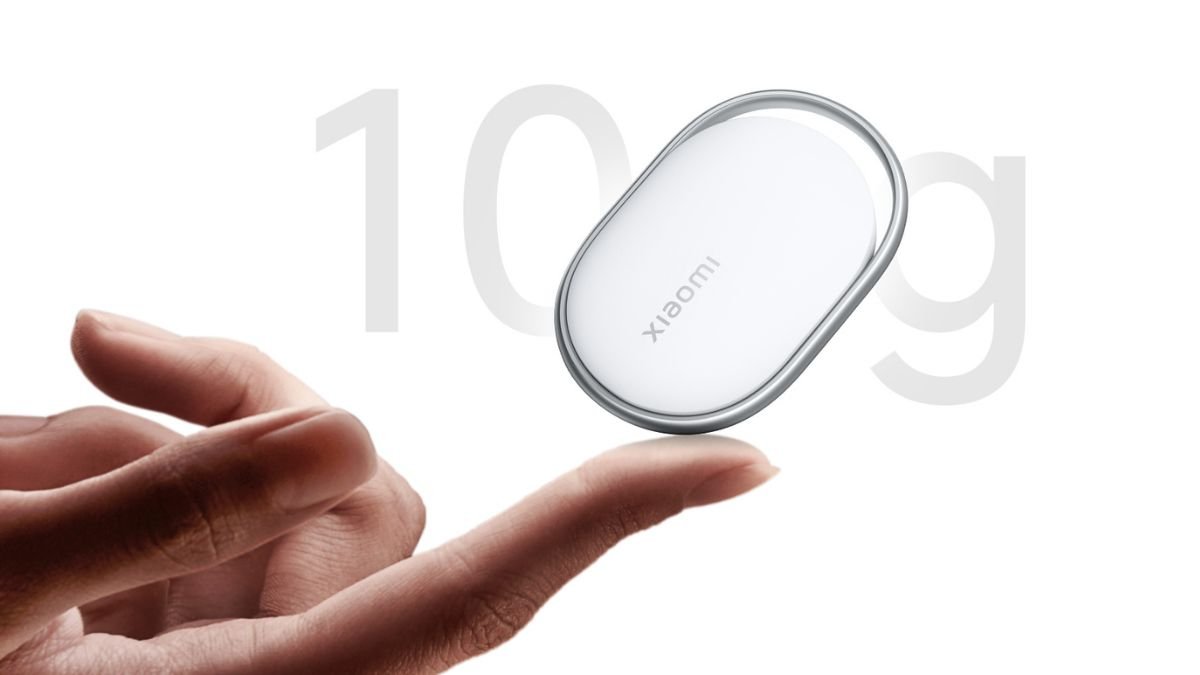
    Xiaomi shared the first official image of the Tag on its X handle. The device is shown in a white colour option. The company confirmed that the tracker will weigh just 10 grams. It will also have a very compact design, making it easy to attach to keys, bags, or other personal items.

    Although Xiaomi has not shared full specifications yet, leaks from an early listing on Xiaomi France’s website reveal more details. The tracker is said to be 7.2mm thick. It will run on a standard CR2032 battery. This battery is user-replaceable and is commonly used in similar devices like the Moto Tag.

    One interesting rumour suggests that Xiaomi Tag could support both Google’s Find My Device network and Apple’s Find My network. If true, this will make it more versatile compared to many existing trackers in the market.

    However, reports also suggest that the standard version of Xiaomi Tag may not include UWB support. UWB, or Ultrawide-band, allows precise location tracking. It helps users find their items with accurate distance and direction guidance. UWB is available in products like the Apple AirTag and the Moto Tag.

    Without UWB, users will have to rely on approximate location tracking instead of precise positioning. There are reports that Xiaomi may launch a UWB-enabled version of the Tag in the future.

    More details about features and pricing will be revealed during the launch event. Early rumours suggest a price of 17.99 euros, which is roughly Rs 2,000.

    Follow Techlomedia on Google News to stay updated. Follow on Google NewsFollow on Google News

    Affiliate Disclosure:

    This article may contain affiliate links. We may earn a commission on purchases made through these links at no extra cost to you.

  • New WhatsApp Exploit Script Listed for Sale on Hacking Forums

    New WhatsApp Exploit Script Listed for Sale on Hacking Forums

    Add Techlomedia as a preferred source on Google. Preferred Source

    A new threat has emerged on underground hacking forums involving the popular messaging app WhatsApp. Security researchers have noticed posts where a cybercriminal claims to be selling a script that can crash WhatsApp and cause other problems for users.

    This script is on sale for just $30, which makes it affordable for most people to buy and use it.

    According to threat intelligence shared online, the seller says the tool can make WhatsApp break on both Android and iPhone devices. On Android phones, the offer claims the exploit can crash the app entirely. On iPhones, the script is said to crash WhatsApp and disrupt group chats.

    The listing on the forum claims the script can send many calls in quick succession to a target, a method often called call bombing. The ad also mentions a feature described as pair spam, though details of how it works were not clear.

    The seller says the script works through Termux, which is a terminal environment for Android devices. This means the exploit may run directly from a phone without the need for advanced infrastructure. The only other requirement is a virtual phone number, which adds anonymity for the attacker.

    It is not clear how the script achieves these effects or whether the exploit affects all versions of WhatsApp. Meta, the company that owns WhatsApp, regularly releases security updates to fix vulnerabilities and improve stability.

    To be safe against such exploits, it is important to keep your WhatsApp unapt. Always install the latest version of WhatsApp from the official app store. Updates often contain important security fixes. You should also enable two step verification in WhatsApp settings. This adds an extra layer of protection to your account.

    Users should also avoid clicking on suspicious links sent by unknown contacts. If the app crashes repeatedly, update it immediately. If the problem continues, reinstall the app after backing up chats.

    Follow Techlomedia on Google News to stay updated. Follow on Google NewsFollow on Google News

    Affiliate Disclosure:

    This article may contain affiliate links. We may earn a commission on purchases made through these links at no extra cost to you.

  • Google Blocks Antigravity Access After Backend Abuse

    Google Blocks Antigravity Access After Backend Abuse

    Add Techlomedia as a preferred source on Google. Preferred Source

    Google has restricted access to its Antigravity AI coding platform after detecting what it described as large-scale misuse of its backend infrastructure. The clarification came directly from Varun Mohan, who is building Antigravity under Google DeepMind. He shared a detailed statement on X explaining why some users were suddenly blocked from the service.

    In his statement, Mohan said the company noticed a massive increase in backend traffic that was not aligned with the intended use of Antigravity. According to him, this surge heavily impacted compute resources and degraded the experience for genuine users. Because of this, Google decided to quickly block access for accounts that were not using the product as designed.

    The issue appears to be linked to developers connecting Antigravity through third-party tools, especially OpenClaw. These tools allowed users to route authentication tokens and automate workflows using Antigravity’s backend. However, using the backend as a proxy layer for other products goes against the platform’s terms of service.

    Mohan clarified that the restriction only affects Antigravity. Other services from Google and its AI ecosystem are not impacted. He also acknowledged that some users may not have realized they were violating the rules. He added that Google will provide a path for certain users to regain access, but the company had to act fast to protect overall service quality.

    From a business and infrastructure standpoint, the move makes sense. AI infrastructure is expensive and resource-intensive. If a group of users starts routing large volumes of traffic in unintended ways, it can affect stability for everyone else. Protecting paying and legitimate users becomes the top priority.

    At the same time, this situation shows a growing challenge in the AI ecosystem. Developers want flexibility. They want to connect tools, automate workflows, and experiment with AI agents. Platform providers want tighter control over how their infrastructure is accessed and monetized. When expectations are not clearly aligned, friction is bound to happen.

    This enforcement was expected, but communication could have been smoother. Sudden blocks without structured warnings can frustrate even genuine developers. As AI platforms continue to grow, clearer policies and better integration guidelines will become essential.

    This episode also shows that major AI companies are becoming stricter about backend usage. Going forward, developers may need to rely more on official APIs and approved integrations instead of creative workarounds.

    For now, Google’s message is straightforward. Antigravity is meant to be used as a product, not as a backend relay system.

    Follow Techlomedia on Google News to stay updated. Follow on Google NewsFollow on Google News

    Affiliate Disclosure:

    This article may contain affiliate links. We may earn a commission on purchases made through these links at no extra cost to you.

  • jsPDF Vulnerability Exposes Developers to Serious PDF Object Injection Risk

    jsPDF Vulnerability Exposes Developers to Serious PDF Object Injection Risk

    Add Techlomedia as a preferred source on Google. Preferred Source

    A newly disclosed security issue in the popular jsPDF library has raised serious concerns for web developers. The flaw could allow attackers to inject malicious objects into PDF files generated by web applications. The vulnerability is tracked as CVE-2026-25755 and carries a CVSS score of 8.8, which makes it a high-severity issue.

    jsPDF is widely used by developers to create PDF files directly in the browser. Many websites use it to generate invoices, reports, tickets, and other downloadable documents.

    The issue was discovered by security researcher ZeroXJacks. The researcher also released a proof of concept showing how a crafted payload inside the addJS method can trigger custom actions when the PDF is opened.

    The issue exists in the addJS method. This method allows developers to embed JavaScript inside a generated PDF file. The problem happens because user input is not properly cleaned before being added into the PDF structure. In the affected code, user supplied text is directly inserted into the PDF stream without escaping special characters.

    The vulnerable line looks like this:

    this.internal.out("/JS (" + text + ")");

    In PDF format, parentheses are used to define strings. If an attacker adds a closing parenthesis inside the input, it can break out of the intended string and inject new PDF objects.

    This means attackers can insert their own PDF structure and actions inside the document. Attackers could icy document metadata, inject fake annotations, alter digital signature sections, encrypt parts of the file, or trigger automatic actions when the PDF opens.

    This is not a normal web-based cross-site scripting attack. Instead of attacking the browser, this vulnerability manipulates the internal object structure of a PDF file. This makes the attack more dangerous in some cases.

    Even if JavaScript is disabled in the PDF viewer, injected PDF actions like /OpenAction can still run automatically when the document is opened.

    Any web application that dynamically generates PDF files using jsPDF and includes user supplied input in the addJS method is at risk. This is especially dangerous for platforms that generate invoices or reports from user data or allow custom PDF exports. Since jsPDF is widely used, millions of developers could be affected.

    Developers should immediately update to jsPDF version 4.1.0 or later. In this version, input is properly sanitized and special characters like parentheses and backslashes are escaped correctly. Until applications are updated, developers should avoid embedding untrusted input using the addJS method.

    Follow Techlomedia on Google News to stay updated. Follow on Google NewsFollow on Google News

    Affiliate Disclosure:

    This article may contain affiliate links. We may earn a commission on purchases made through these links at no extra cost to you.

  • Your voice now fully controls this AI browser

    Your voice now fully controls this AI browser

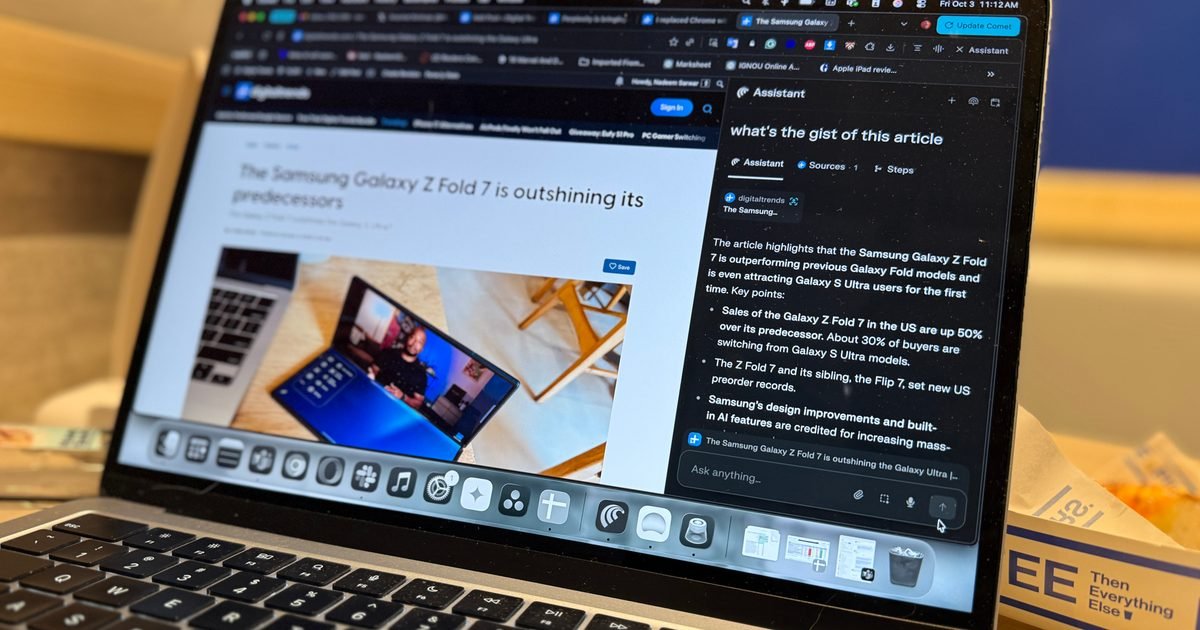
    Perplexity just flipped the switch on an upgraded voice mode for its Comet browser. Desktop users can try it right now. iOS users wait a few more days. The update lets you control everything hands free. Open sites, scroll pages, or follow links. All by talking.

    On desktop you hit Shift + Alt + V, or Shift + Option + V on a Mac. On iPhone the same tools arrive soon, turning Comet into what might be the first mobile browser you never have to touch.

    The feature runs on OpenAI’s latest real time model. CEO Aravind Srinivas announced the rollout on X and thanked OpenAI’s multimodal team. The goal is full browser navigation through speech, not just voice search.

    Built on OpenAI’s latest voice tech

    This voice mode uses OpenAI’s gpt-realtime-1.5 model, built for low-latency voice agents. Srinivas credited OpenAI’s team, and Perplexity claims it improved tool-call stability by more than 25 percent. That means fewer misfires when you ask the browser to actually do something. The voices also sound better, with pacing that works for longer listening sessions.

    We’re rolling out an upgraded voice mode on Comet. It’s the first time you can fully control the browser hands free. Comet iOS will come with this upgrade voice mode in a few days. Pre order if you haven’t yet!
    pic.twitter.com/gjRBQqRtb9

    — Aravind Srinivas (@AravSrinivas) February 24, 2026

    Why full voice control matters now

    Most browsers treat voice like a party trick. You speak a query, results show up, then you tap. Comet wants voice to carry you through the whole session. Ask about whatever is on your screen. Try saying “scroll down, open the third link, summarize this page, compare it to the tab on the left.” No keyboard required.

    The timing fits the shift toward ambient computing. Perplexity is betting the web works better when you talk to it. On desktop the feature is live now.

    Comet also takes a different privacy stance. It processes voice locally when possible and doesn’t store click histories in the cloud by default. No ad tracking profiles built from your browsing.

    What to watch for in the coming days

    Desktop users can test the voice mode starting today. For iOS it lands around March 11 based on App Store pre-order listings. The real question is whether the controls feel natural across real tasks, not just demos.

    Perplexity is already building more. Comet Assistant learns your preferences and can help with shopping, ordering food, or finding flights based on what you usually do. A password manager and cross-device sync are in the works. Android users are waiting on those. For iOS this voice upgrade is just the first step.

  • King of Meat to Shut Down on April 9, Amazon Games Confirms Full Refund for Players

    King of Meat to Shut Down on April 9, Amazon Games Confirms Full Refund for Players

    Add Techlomedia as a preferred source on Google. Preferred Source

    In a surprising move, Amazon Games has confirmed that King of Meat will shut down on April 9, 2026. The four player co-op combat game will remain playable until that date. After that, the servers will go offline and the game will no longer be accessible.

    The announcement was shared by Amazon Games, which published the title, along with developer Glowmade. The companies also confirmed that everyone who purchased the game will receive a full refund through their respective platform providers in the coming weeks.

    King of Meat originally launched on October 7, 2025 for PlayStation 5, Xbox Series consoles, and PC via Steam. A Nintendo Switch version was planned for early 2026, but that version will now likely never see the light of day.

    In its official message, Amazon Games said that while the team was proud of the creativity and innovation behind King of Meat, the game did not reach the audience they expected. That line says a lot.

    King of Meat tried to stand out with chaotic arena style combat and a colorful world. It was designed as a fun and competitive co-op experience. But in today’s market, launching a new multiplayer game is extremely difficult. Players already spend most of their time on established titles like Fortnite, Call of Duty: Warzone, and Apex Legends. Breaking into that space requires either a massive hook or strong long term support.

    It is possible that King of Meat struggled with player retention. Many multiplayer games see strong interest at launch but fail to maintain an active community after the first few weeks. If matchmaking becomes slow or repetitive, players move on quickly.

    There is also the bigger issue of live service fatigue. Over the past few years, we have seen many online games shut down due to low engagement. Even games backed by big publishers are not safe. The cost of running servers, pushing updates, and marketing the game is high. If the numbers do not justify the investment, publishers often pull the plug early.

    The most interesting part of the announcement was the full refund for all buyers. That is not something we see every day. Usually, live service games that shut down do not offer blanket refunds unless they are in early access or have just launched. This suggests that the game may not have met internal expectations in terms of sales or active users. Offering refunds could also be a way to maintain goodwill among players, especially for future Amazon Games projects.

    Follow Techlomedia on Google News to stay updated. Follow on Google NewsFollow on Google News

    Affiliate Disclosure:

    This article may contain affiliate links. We may earn a commission on purchases made through these links at no extra cost to you.

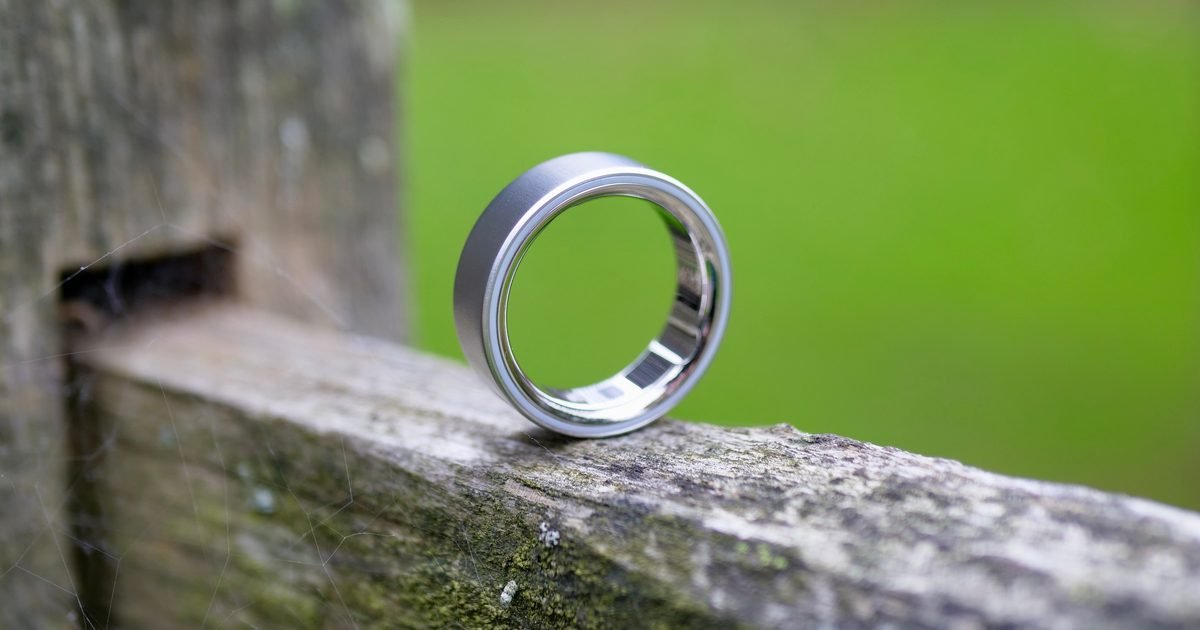
  • Oura’s smart ring AI promises more personalized women’s health support

    Oura’s smart ring AI promises more personalized women’s health support

    Oura has gradually become one of the top health-focused wearable manufacturers, and its rise can be attributed to a combination of excellent hardware and a strong focus on research and development aimed at accurate health tracking.

    In 2024, Oura released its health coach, Oura Advisor, which is an AI-powered health coach that answers questions about health and wellness using data collected from your Oura Ring. Stepping ahead in that direction, Oura has now announced its proprietary AI model focusing on women’s health. It analyzes women’s biometric data and long-term trends to provide personalized, evidence-based insights tailored to the user.

    What’s different about Oura’s new proprietary large language model?

    Oura’s new proprietary large language model differs from other AI providers, primarily in its training dataset. The custom model is trained on trusted medical research and standards rigorously vetted by OURA’s board-certified clinicians and women’s health experts. 

    The model is designed for women. When women ask health-related questions, it draws on curated women’s health research from verified, trusted sources. Combining it with user data collected from the Oura ring, it evaluates relevant biometric data and long-term patterns across sleep, activity, menstrual cycle, pregnancy metrics, and other data to deliver accurate, reliable insights.

    “By designing a model specifically for women and grounding it in trusted clinical science and real-world biometric data, we’re setting the standard for how responsible intelligence should be built and expanded across more areas of health, pairing rigorous science with the lived, longitudinal data that makes ŌURA uniquely powerful,” said Ricky Bloomfield, MD, chief medical officer at Oura.

    What happens to your data?

    Oura has said that the company believes advancements in AI should not come at the cost of user data. The model is hosted entirely on Oura’s controlled infrastructure, ensuring that user data is not shared with other AI models.

    If one decides to participate, their data will be used to train the AI and improve its performance, but Oura will never share or sell the data to a third party. If a user is not comfortable with sharing their personal data, they can always opt out or choose not to join.